

Passwords are slowly losing their role as the default way to sign in. In 2026, passkeys are supported across the major operating systems, browsers, password managers, and a growing number of websites and apps. They can make sign-in faster, but the real advantage is security: a properly implemented passkey is tied to the legitimate website or app, so there is no reusable password for a phishing page to steal.
This guide explains how to start using passkeys without locking yourself out, how to choose where they should be stored, how to set them up with Google, Apple, Microsoft, Windows, Android, iPhone, and common browsers, and how to build a recovery plan before you remove old sign-in methods. It also covers the parts that short setup guides often skip: synced versus device-bound passkeys, cross-device QR sign-in, shared devices, work accounts, security keys, lost phones, migration between ecosystems, and the mistakes that can turn a good security upgrade into an account-recovery problem.
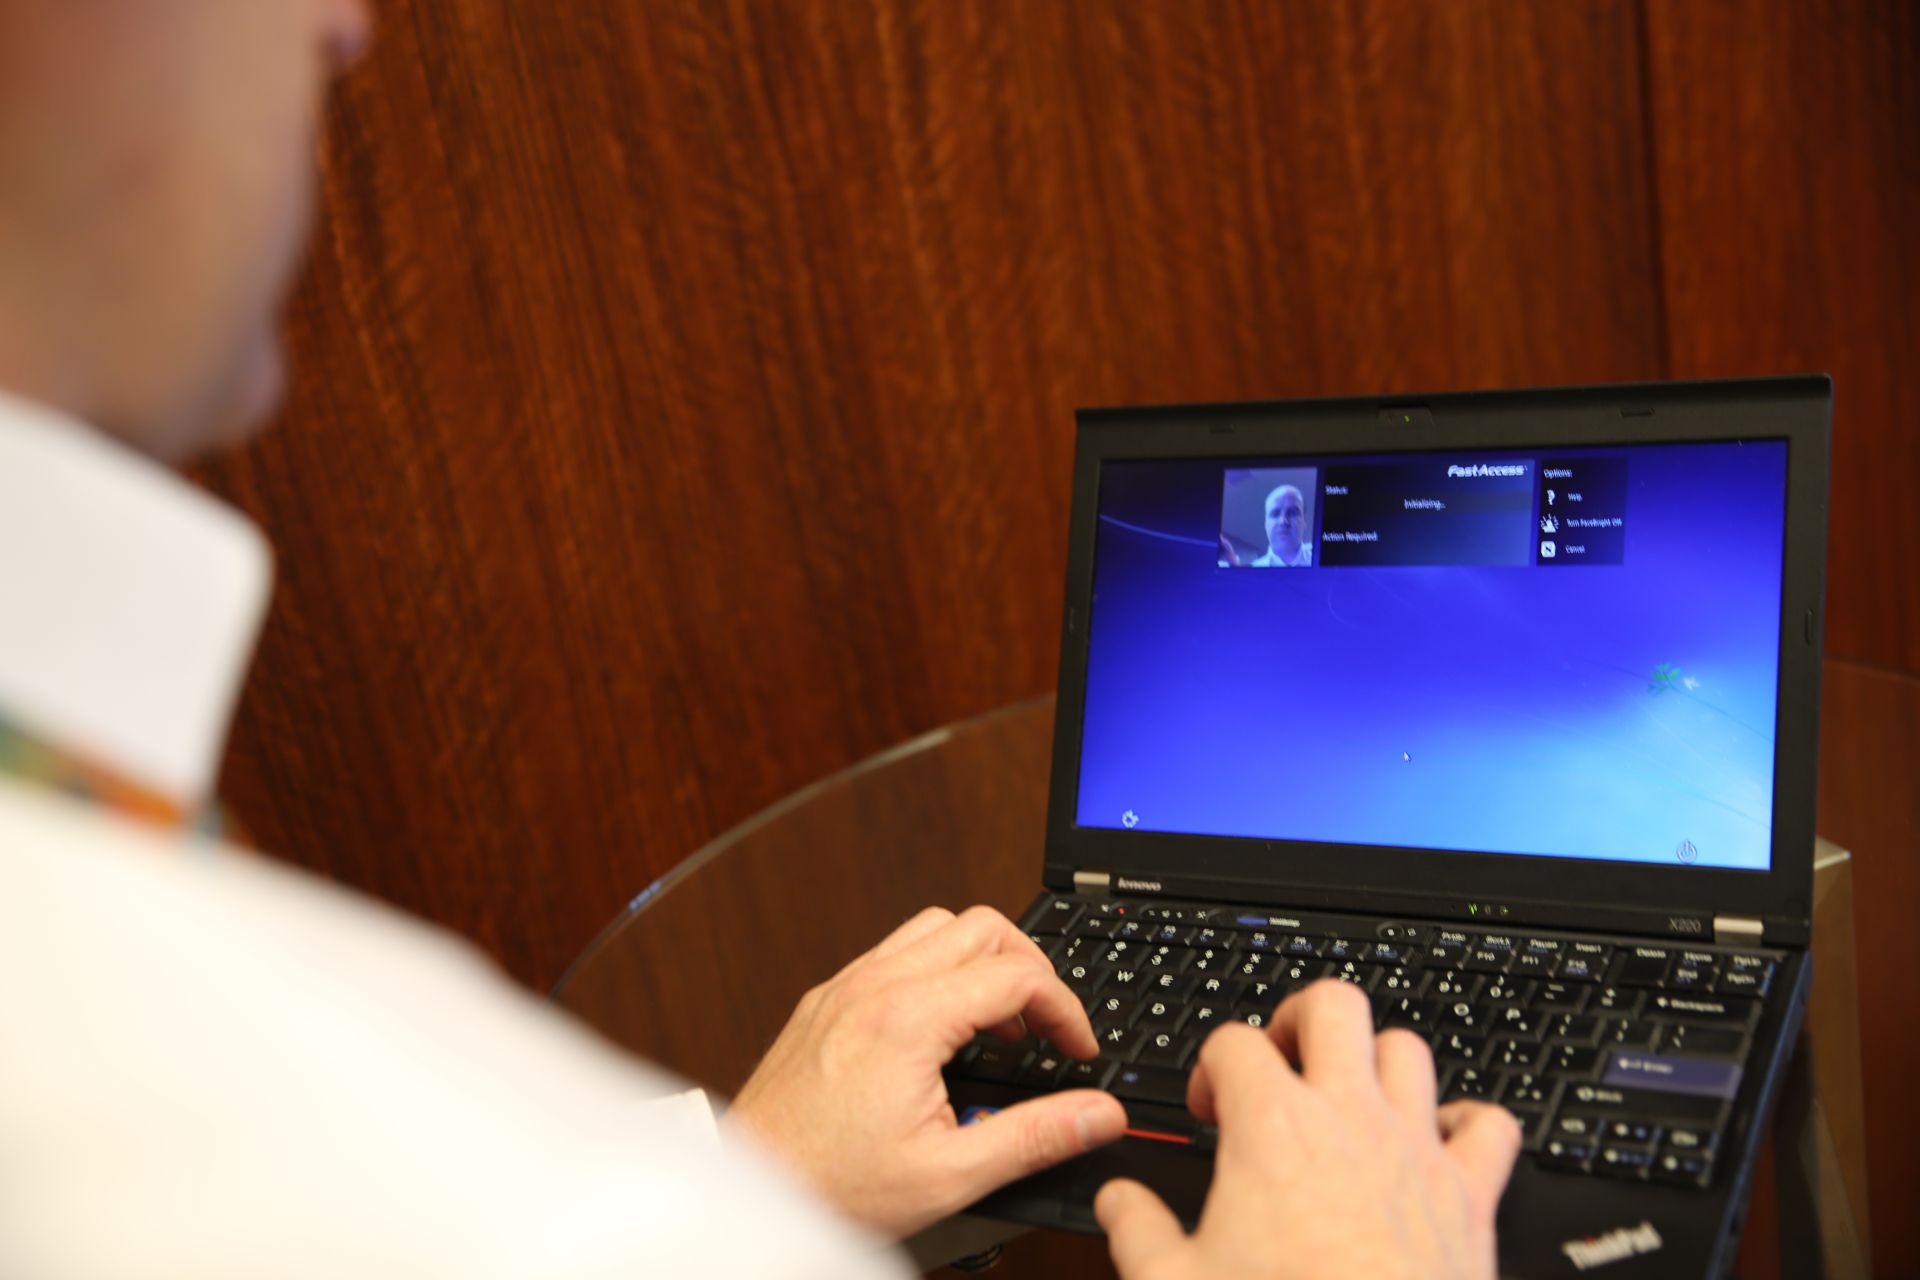 Device authentication such as face recognition, fingerprint recognition, or a local PIN can unlock a passkey without revealing a reusable password. Photo: Intel Free Press, CC BY-SA 2.0, via Wikimedia Commons.
What a passkey actually is
A passkey is a FIDO credential used to authenticate to a specific website or application. Instead of proving your identity by sending a shared secret such as a password, your device uses public-key cryptography. The service stores a public key, while the corresponding private credential remains protected by your device or credential manager. When you sign in, the service sends a challenge and your device proves possession of the credential after you approve the action with the device’s normal unlock method.
That distinction matters because the private credential is not something you type into a webpage. A convincing fake login page can trick a person into entering a password or one-time code, but a passkey is designed to work only with the legitimate service it was created for. The FIDO Alliance describes passkeys as phishing-resistant credentials built on FIDO standards, while CISA recommends organizations move toward phishing-resistant forms of authentication such as FIDO/WebAuthn where possible.
A passkey is also not the same thing as your fingerprint, face scan, or device PIN. Those are local methods used to authorize access to the passkey. Your biometric information normally stays on the device. Google, for example, states that biometric data used to unlock a passkey is not shared with Google. Apple similarly stores passkeys in iCloud Keychain and protects that data with end-to-end encryption. Microsoft supports passkeys stored locally with Windows Hello, on security keys, on phones and tablets, and in synced credential managers.
Why passkeys are worth using in 2026
There are three practical reasons to adopt passkeys. The first is resistance to phishing. A passkey is associated with the legitimate domain or application, so a fake site cannot simply collect it the way it can collect a password. The second is resistance to password reuse. Each passkey is unique to the service, eliminating the familiar problem in which a breach at one site exposes a password that is reused elsewhere. The third is usability. On a properly configured device, signing in can be as simple as approving a Face ID, fingerprint, Windows Hello, Android screen-lock, or PIN prompt.
Passkeys have also moved beyond an experimental feature. The FIDO Alliance’s 2026 research reported billions of passkeys in active use and broad consumer awareness, while Microsoft, Google, and Apple all provide native passkey support. That does not mean every website supports them or that every deployment behaves identically. It means passkeys are mature enough that most people can begin using them for important accounts while keeping sensible recovery options.
The biggest mistake is to think of the transition as “delete all passwords today.” A safer approach is incremental. Add a passkey to an account, test it from the devices you actually use, confirm your recovery email, phone, backup codes, trusted devices, or other recovery methods, and only then decide whether it makes sense to remove or de-emphasize the old password. Some services still keep a password behind the scenes even after you create a passkey. Others let you become effectively passwordless. Treat each account according to its actual settings rather than assuming every service works the same way.
Step 1: Check your devices before creating your first passkey
Start with the devices you trust and use regularly. A passkey relies on a secure device unlock mechanism, so make sure your phone, tablet, or computer has a screen lock configured. On a phone, that normally means a PIN, passcode, fingerprint, or face unlock. On Windows, it may be Windows Hello with a PIN, fingerprint, or compatible camera. On Apple devices, it may be a device passcode with Touch ID or Face ID.
Update the operating system and browser before you begin. Older releases can have incomplete passkey support, especially for cross-device sign-in or newer credential-manager features. Microsoft currently lists support across modern Windows, macOS, ChromeOS, iOS, Android, Edge, Safari, and Chrome versions, but the exact minimum versions can change. If you are supporting a family member, employee, or older computer, check the current vendor documentation instead of assuming the menu shown on your own device will be identical.
Then ask a less obvious question: who else can unlock the device? A passkey usually considers successful device unlock to be authorization to use the credential. If several people know the same tablet PIN, or a shared family computer has one common login, storing a passkey there may give more people access to the account than you intend. The strongest cryptography cannot compensate for a device unlock code that everyone in a household knows.
 A device PIN can be the local approval method used to unlock passkeys. Image: Mykhal, CC0, via Wikimedia Commons.
Step 2: Decide where your passkeys should live
When a website offers to create a passkey, the most important decision may be the save location. A passkey can be stored in a synced credential manager, locally on one device, on a phone or tablet, or on a compatible FIDO2 hardware security key. The right choice depends on whether you value convenience, portability, platform independence, or tighter control.
Use a synced credential manager for everyday convenience
For most consumers, a synced credential manager is the easiest starting point. Apple can synchronize passkeys through iCloud Keychain. Google Password Manager can store passkeys for a Google Account and make them available on supported signed-in devices. Microsoft Password Manager and other credential managers can do the same within their supported environments. Third-party password managers may also support passkeys.
The advantage is resilience. If your passkey exists only on one laptop and that laptop fails, you need another recovery route. A synced manager can make the passkey available on another approved device after you sign in and restore the credential manager. This is why Microsoft recommends using a synced credential manager whenever possible for normal use. The trade-off is that the security and recovery of the credential-manager account become especially important.
Use a device-bound passkey when you intentionally want it tied to one device
A device-bound passkey stays on the device or hardware token where it was created. This can be useful in high-assurance environments, for administrators, or when an organization intentionally avoids cloud synchronization. It can also be inconvenient if the device is lost, damaged, reimaged, or replaced. If you choose a device-bound passkey, create a second independent sign-in method before you depend on it.
Use a hardware security key when you want a physical credential
Compatible FIDO2 security keys can store passkeys. They are useful for people at higher risk of targeted phishing, for administrative accounts, and for users who want a physical credential that can move between devices. A good operational pattern is to register two keys, keep one with you, and store the second securely in a different location. Do not keep both on the same keyring or in the same laptop bag, because a single loss would remove both copies.
Step 3: Build your recovery plan before removing anything
Passkeys are designed to remove the weak points of passwords, but account recovery still matters. Before you change sign-in methods, open the security settings for the account and list every recovery route that still works. Common examples include a recovery email, recovery phone number, backup codes, a second trusted device, a second passkey, a security key, or organization-managed recovery.
Do not assume that a recovery phone number is automatically sufficient. If the phone is lost together with the SIM, you may temporarily lose access to both the passkey and the recovery channel. Likewise, a recovery email is useful only if you can access that mailbox independently. The goal is not to accumulate dozens of methods; it is to avoid a single point of failure.
A simple test is to imagine that your primary phone disappears tonight. Could you still sign in from another device? Could you recover the Apple, Google, Microsoft, or third-party credential manager that holds your passkeys? Do you know where your backup codes are stored? If the answer is no, fix that before you start deleting old credentials.
For important accounts, keep recovery information offline or in an independently secured location. A printed set of backup codes stored securely can be more useful during a device-loss emergency than a screenshot saved only on the lost phone. Avoid storing your only recovery codes in the same password manager whose account you are trying to recover.
Step 4: Create a passkey for your Google Account
Google allows users to sign in to a Google Account with a passkey using a fingerprint, face scan, or device screen lock. Creating a passkey does not automatically remove the account’s existing authentication or recovery methods. That makes Google a useful place to practice because you can add the passkey first and verify that it works before changing anything else.
- Sign in to your Google Account from a trusted personal device.
- Open the account’s security or passkey settings using Google’s official account pages rather than a link from an unsolicited email or message.
- Choose the option to create a passkey.
- Review where the passkey will be stored. If the browser offers more than one credential manager, choose deliberately rather than accepting the first prompt without reading it.
- Approve creation using the device’s fingerprint, face unlock, PIN, or other screen-lock method.
- Sign out in a separate browser session or use another trusted device and test the new passkey.
If your Google Account uses 2-Step Verification, Google explains that a passkey can satisfy the possession requirement and bypass the separate second step for that sign-in because the device possession and local unlock provide the verification. This is normal behavior; it does not mean two-step protection has been turned off globally.
Google Password Manager can store passwords and passkeys and make them available across supported devices where you are signed in with the same Google Account. If you use multiple Google Accounts on Android, pay attention to the account selected when saving the credential. Saving a passkey to the wrong personal or work profile can create confusion later.
Step 5: Create and use passkeys on iPhone, iPad, and Mac
Apple’s passkey experience is built around iCloud Keychain and the Passwords system. Apple states that passkeys are encrypted in iCloud Keychain and available across devices signed in to the same Apple Account when the necessary security features are enabled. On current Apple software, make sure iCloud Passwords & Keychain synchronization is enabled and two-factor authentication is active for the Apple Account.
When a supported website or app offers to create a passkey on iPhone or iPad, follow the service’s account-security flow, choose the passkey option, and approve the save with Face ID, Touch ID, or the device passcode. The passkey can then be used on other Apple devices connected to the same account and keychain.
Apple also supports using an iPhone to sign in on a nearby non-Apple device. If you are changing devices or Apple Accounts, you can also review LordAI’s guide to signing out of an Apple Account safely before removing a trusted device. The website or app on the computer may offer an option such as “passkey from nearby device.” It displays a QR code, which you scan with the iPhone. The devices use proximity checks, commonly including Bluetooth, and the iPhone authorizes the sign-in without copying the private credential into the computer you are borrowing.
This is especially useful on a temporary machine. If you are using a public computer, a family member’s PC, or another device that you do not control, do not choose a save option that stores the passkey on that computer. Use the nearby-device path instead, finish the session, sign out of the website, and close the browser. Avoid creating passkeys on untrusted machines unless the flow explicitly saves the passkey back to your phone or chosen credential manager rather than locally.
If you later need to delete a passkey from Apple’s Passwords app, confirm that you still have another working sign-in method first. Deleting a passkey from a synchronized keychain may remove access to it across your devices, not just from the screen in your hand.
 Passkeys depend on the security of the device that stores or unlocks them. Photo: C.Stadler/Bwag, CC BY-SA 4.0, via Wikimedia Commons.
Step 6: Set up passkeys for a Microsoft account
Microsoft supports passkeys for personal Microsoft accounts, work or school accounts when the organization permits them, and other websites that support passkeys. For a personal Microsoft account, the official support flow directs users to Advanced Security Options, where they can add a new way to sign in or verify and choose a face, fingerprint, PIN, or security-key method.
- Open your Microsoft account using an official Microsoft domain and sign in normally.
- Go to Advanced Security Options.
- Choose to add a new sign-in or verification method.
- Select the passkey-capable option offered for your device, such as Face, Fingerprint, PIN, or Security Key.
- When prompted, review the storage location. Microsoft may offer a password manager, a phone or tablet, a security key, or the Windows device through Windows Hello.
- Complete the local device-unlock prompt.
- Test the passkey in a fresh session before deleting an older sign-in method.
Work and school accounts can behave differently because an administrator may control which passkey providers or device types are permitted. If the option is missing on a managed account, do not assume the browser is broken. The organization may not have enabled the feature or may require a specific Authenticator or security-key workflow.
Microsoft’s current support documentation also notes that cross-device flows may rely on a QR code and Bluetooth proximity. If the QR flow fails, check that Bluetooth is enabled on both devices, that they are close together, and that both have internet access. Also check that an old browser or operating system is not the limiting factor.
Step 7: Understand Windows Hello and local Windows passkeys
Windows Hello is not itself the same thing as a passkey, but it can protect and authorize passkeys saved to the Windows device. Depending on the current Windows version and your account configuration, passkeys may be stored locally, synchronized through a supported password manager, or handled by third-party passkey providers.
On supported Windows versions, passkey management is available in Settings under Accounts and Passkeys. Microsoft also provides advanced passkey options where supported credential services can be enabled or disabled. This matters on a computer with several password managers installed, because a passkey prompt may otherwise offer multiple storage destinations.
If you share a Windows computer, create separate Windows user accounts. A passkey stored under your Windows profile should not become a family credential simply because everyone uses the same machine. Separate user profiles provide clearer boundaries for local Windows Hello credentials, browser data, and synced accounts.
Before resetting, reinstalling, or replacing a Windows PC, determine whether an important passkey is local-only or synchronized. A local passkey can disappear with the installation. If the account matters, create another passkey on a second device or confirm that a separate recovery method works before wiping the computer.
Step 8: Use passkeys on Android without mixing up accounts
Android devices can store and use passkeys through supported credential managers, including Google Password Manager and third-party providers. The experience is designed to feel similar to password autofill: when a website or app supports passkeys, Android presents the available credential and asks for local device verification.
Before creating passkeys on Android, make sure the screen lock is enabled and that you know which Google Account or credential provider is active. People with a personal Google Account, a work profile, and multiple password managers can accidentally save a passkey somewhere they do not expect. When the chooser appears, read the account name and provider before approving.
If you plan to replace the phone, verify that the credential manager is synchronizing correctly and that you can sign in to that manager on the new device. Do not factory-reset the old phone the moment the new phone powers on. First test the accounts that matter: primary email, Apple or Google identity, Microsoft account, banking portals, domain registrar, cloud storage, and any administrator accounts.
A successful migration is not proven by seeing the same app icons on the new phone. It is proven when you can authenticate to the services and you know how to recover them if the new device is lost.
Step 9: Learn the cross-device QR-code sign-in flow
One of the most useful passkey features is the ability to use a credential stored on your phone to sign in on another device. This is often called cross-device authentication. The computer displays a QR code, you scan it with the phone, the devices establish that they are physically near each other, and the phone approves the sign-in.
This solves an important problem: you may not want your passkey synchronized into every computer you touch. A hotel business center, a conference computer, a family PC, or a fresh workstation can use the phone’s passkey without receiving the private credential itself.
When the QR flow fails, troubleshoot methodically. Make sure you selected the option for another device rather than a local passkey. Turn on Bluetooth on both devices, keep them physically close, connect both to the internet, and retry in a current browser. If you are on a corporate network with device restrictions, a managed policy may also interfere.
Do not photograph a passkey QR code and send it to someone else. The cross-device flow is designed around proximity and a real-time authentication session. Treat unexpected QR sign-in prompts the same way you would treat unexpected login approval notifications: stop and verify what account and device initiated the request.
Step 10: Keep passwords when they still serve a recovery purpose
“Passwordless” sounds like the obvious finish line, but the correct endpoint depends on the service. Some accounts let you remove a password entirely. Others keep a password as an alternative sign-in method. Some organizations require both a passkey and legacy recovery methods because of policy or compatibility.
Do not remove a password simply because the service has added a passkey button. First verify whether the password is still required for older devices, account recovery, application-specific connections, command-line tools, email clients, or administrative tasks. A password that is no longer used for routine sign-in can still be valuable as a protected fallback if the service requires it.
If you retain the password, make it unique and store it in a reputable password manager rather than memorizing and reusing it. The purpose of the passkey transition is not to replace one fragile habit with another. You can use passkeys for routine sign-in while keeping a long, unique password as a rarely used fallback where the service requires one.
Step 11: Create a “two-path” recovery design for your most important accounts
For high-value accounts, aim for two independent ways to recover access. Independence is the key word. A passkey on your phone plus a recovery email that is accessible only through the same phone is not truly two paths. A stronger design could be a synced passkey on your phone and laptop plus printed backup codes in secure storage, or a passkey in your credential manager plus a hardware security key kept separately.
Your identity-provider account deserves special attention because it may unlock everything else. If Google Password Manager stores your passkeys, protecting the Google Account becomes foundational. If iCloud Keychain stores them, your Apple Account and trusted-device recovery become foundational. If a third-party manager stores them, protect its master account and emergency recovery method.
Think of this as a dependency map. Email can reset shopping accounts, social media, cloud tools, and financial services. A phone number may reset email. A device may unlock the credential manager. If all roads lead to the same phone, the system looks redundant on paper but can still fail from one lost or stolen device.
Step 12: Treat shared and public devices differently
A passkey makes it easy to authenticate, which means you must be deliberate about where you save it. On a public, borrowed, or shared computer, avoid selecting a local save option. Use your phone’s nearby-device flow when available. If the site only supports local creation, wait until you are on a trusted device unless access is urgent and you understand how to remove the credential afterward.
After signing in on a public computer, sign out of the website explicitly. Do not rely on closing the browser window. If the service offers a “sign out of all sessions” page, review it later from a trusted device. Also check the account’s list of registered passkeys. An accidentally created passkey on a public computer may remain a valid sign-in method even after the browser session is closed.
Work computers require another layer of judgment. Your employer may manage the device, browser, credential manager, and local account. A personal passkey stored on a corporate device can become inaccessible when the device is reimaged or you leave the company. Prefer a personal phone or personal credential manager for personal accounts, subject to the organization’s rules.
Step 13: Know when a hardware security key is the better choice
Synced passkeys are convenient for most people, but a physical security key can be valuable when the consequences of compromise are unusually high. Examples include domain registrar access, cryptocurrency custody interfaces, administrator accounts, code repositories, cloud infrastructure, executive email, and accounts belonging to journalists, activists, or people facing targeted attacks.
A hardware key provides a clear physical boundary. The credential does not silently appear on every device logged into your cloud account. That can reduce some classes of account-recovery and synchronization risk. The cost is operational discipline: you must have a spare, know where it is, and register both before an emergency.
When buying a key, confirm that it supports the current FIDO2/passkey requirements of the service you intend to protect. Do not purchase a random “security USB” product based on appearance alone. Follow the service’s official compatibility guidance and buy from reputable sellers to reduce the risk of counterfeit or unsupported hardware.
Step 14: Migrate to a new phone without losing access
Phone migration is where users discover whether their passkeys are truly synchronized. Do not treat the old phone as disposable until authentication has been tested on the new one. Keep both devices charged and connected while you validate the transition.
- Sign in to the operating-system account and credential manager on the new phone.
- Wait for passwords and passkeys to synchronize.
- Open the credential manager and confirm that important accounts appear.
- Test sign-in to your primary email and identity-provider account first.
- Test two or three unrelated services that use passkeys.
- Check your recovery phone, email, backup codes, and security keys.
- Only after successful testing should you erase, trade in, or sell the old phone.
If a passkey does not appear, do not immediately delete it from the account’s website. First identify where it was stored. It may be in a different credential manager, a different Google or Apple account, a work profile, or local storage on the old device. Create a new passkey on the new phone while you still have access through the old one, then remove obsolete credentials after the new route is proven.
Step 15: Handle a lost or stolen phone in the right order
If a phone containing passkeys is lost, the first goal is to secure the device and the account ecosystem that can restore those credentials. Use the platform’s official lost-device tools from another trusted device. Change or revoke credentials only after understanding what remains synchronized and which devices are trusted.
A locked phone is not automatically an exposed passkey. Passkeys are protected by the device’s security and credential manager. However, a stolen unlocked phone or compromised device passcode changes the risk. In that case, use your account provider’s device-management page to remove or sign out the missing device, review recent security activity, and rotate recovery details if necessary.
After regaining access, review the passkeys registered with your important accounts. Delete credentials associated with devices you no longer control if the service distinguishes them. Then create fresh credentials on your replacement device and test them.
Step 16: Audit your passkeys twice a year
Passkeys reduce the maintenance burden of passwords, but they should not become invisible forever. Twice a year, open the security settings for your most important accounts and review the registered passkeys, trusted devices, security keys, recovery emails, and phone numbers.
Remove credentials tied to old phones, old computers, former employees, temporary test devices, or credential managers you no longer use. Update recovery details that have changed. Confirm that backup codes are still available and that the account does not depend on a phone number you no longer control.
This audit is especially important for people who test multiple password managers. It is easy to create duplicate credentials in several ecosystems during experimentation. Fewer, well-understood passkeys are easier to recover and revoke than a long list of mysterious device names.
How to tell whether a passkey setup is working correctly
A good passkey setup has several observable signs. You can sign in from your normal device without entering the account password. The browser or operating system shows a device-authentication prompt rather than asking you to type a secret into the website. Your credential manager shows the passkey under the expected account. You can also sign in from at least one backup route, such as another synchronized device, a second passkey, or a security key.
Test the failure path as well as the success path. Open a different browser profile or another device and see what the service offers. If the only working path is the phone in your hand, your recovery design is incomplete. If every device prompts a different credential manager and you do not know where the credential lives, simplify before adding more accounts.
Do not intentionally test by entering credentials into suspicious websites. Phishing resistance is a property of the protocol, not a challenge to experiment with on malicious pages. Use official service domains and your own controlled devices.
Common passkey mistakes and how to fix them
Mistake: creating the passkey in the wrong credential manager
If multiple managers are installed, the save prompt may default to one you do not normally use. Before creating the credential, read the provider name. If you already saved it in the wrong place, create a new passkey in the correct manager, test it, and only then delete the unwanted one from the account.
Mistake: deleting the password before testing another device
Do not remove an old sign-in method until the new passkey works from your real devices and a recovery route has been confirmed. If the service supports a passwordless account, make the transition after the passkey is proven, not before.
Mistake: assuming passkeys automatically move to a new phone
They usually move only if they are stored in a synchronized credential manager and that manager is restored correctly. Device-bound passkeys do not automatically move. Keep the old device until the new sign-in is tested.
Mistake: sharing a device PIN
If other people know the PIN that unlocks your device, they may be able to authorize your passkeys. Change the PIN, use separate user profiles where available, and do not store sensitive passkeys on communal devices.
Mistake: confusing a passkey with a one-time code
A passkey is not a six-digit code that you read and type. If a caller or message asks you to “send your passkey,” treat that as a warning sign. Legitimate passkey authentication happens through the device or credential manager.
Mistake: approving unexpected authentication prompts
Phishing-resistant authentication reduces one type of attack, but you should still reject login attempts you did not initiate. A surprising QR code, security prompt, or device-approval request can be part of another account-takeover attempt.
Mistake: storing every recovery method in the same place
A synchronized password manager, recovery email, and backup codes are not independent if all of them are accessible only through one phone. Separate at least one recovery route physically or logically.
Passkeys versus passwords, authenticator codes, and SMS
| Method | What the user provides | Phishing resistance | Main weakness |
|---|---|---|---|
| Password | A memorized or stored secret | Low | Can be stolen, reused, guessed, or entered into fake sites |
| Password + SMS code | Password plus code sent to phone | Limited | Codes can be phished; phone-number attacks and interception remain concerns |
| Password + authenticator code | Password plus rotating app code | Better than password alone but still phishable | A fake site can sometimes relay the password and code in real time |
| Passkey | Device approval using a protected cryptographic credential | High by design | Requires sound device security and recovery planning |
| FIDO2 hardware key | Physical key plus local approval when required | High by design | Physical loss if no spare or recovery path exists |
The table does not mean that an authenticator app is useless. If a service does not support passkeys or other phishing-resistant FIDO authentication, app-based two-factor authentication is usually a strong improvement over password-only sign-in. CISA’s guidance similarly emphasizes using the strongest available MFA while planning a move toward phishing-resistant methods.
Passkeys for families
Families should resist the temptation to use one shared credential for everything. Each adult should have a separate account where the service supports it, and shared household services should use the platform’s family or sharing features rather than exchanging personal account credentials.
Apple supports shared password groups that can include passwords and passkeys for trusted contacts. Other password managers may have family-sharing features. Use the built-in sharing mechanism instead of sending screenshots or telling someone your device PIN. A shared credential should be shared intentionally and revocably.
For children or older relatives, document the recovery design in a secure family record. The goal is not to give everyone unrestricted access; it is to avoid a situation where the only person who knows how an account works becomes unavailable. Keep the plan simple enough that the designated trusted person can follow it during an emergency.
Passkeys for small businesses
Businesses should treat passkeys as an identity-management project rather than a browser setting. Start with administrator accounts, email, cloud storage, code repositories, payroll, finance tools, and remote access. Determine which services support phishing-resistant authentication and whether the organization can enforce it through its identity provider.
Create an offboarding process before broad deployment. When an employee leaves, the company must be able to revoke passkeys, devices, sessions, and recovery methods without depending on the former employee’s personal phone. Use organization-controlled accounts and managed credential policies for business systems wherever possible.
Also separate consumer-style synced passkeys from device-bound enterprise credentials. Both are passkeys, but they have different operational properties. A company handling regulated or highly sensitive data may prefer device-bound credentials, managed authenticators, or hardware keys for privileged roles. A small team with lower risk may prioritize synchronized passkeys to reduce support burden. The correct policy depends on risk, recovery, device management, and regulatory requirements.
How passkeys improve phishing defense without making you invincible
Passkeys solve a specific and important problem: they make it much harder to steal a reusable sign-in secret through a fake login page. They do not solve every form of fraud. An attacker can still manipulate a user into sending money, installing remote-access software, changing recovery information, sharing screen contents, or authorizing a transaction after login.
Keep normal security habits. Navigate to important sites using saved bookmarks or official apps. Do not trust urgent login links from messages. Keep devices updated. Protect email because it is often a recovery channel. Review account alerts. Use separate user accounts on shared computers. Lock devices when unattended. A passkey strengthens authentication; it does not replace judgment.
What to do when a website does not support passkeys
Use the strongest method the site actually offers. Create a long, unique password and store it in a reputable password manager. Enable multi-factor authentication, preferably an authenticator app, security key, or other stronger method rather than SMS when the service provides choices. Save recovery codes securely.
Do not create a homemade “passkey” by saving a random PIN in a note. Passkey is a specific FIDO-based authentication method. A website either supports it or it does not. Marketing language can be confusing, so look for official documentation that explicitly refers to passkeys, WebAuthn, FIDO2, or a compatible security-key method.
A practical 30-minute passkey rollout plan
If this guide feels long, the implementation can still be simple. Spend the first five minutes checking your device lock, software updates, and credential manager. Spend the next five minutes confirming recovery email, phone, backup codes, and a second device. Then add passkeys to your three most important accounts: your primary email or identity provider, your main cloud account, and one service you use frequently.
Use another ten minutes to test sign-in from a second device and to practice the nearby-device QR flow. In the final five minutes, review the registered passkeys and label or remove anything you do not recognize. Do not delete old passwords or recovery methods during this first session unless you are certain the service’s passwordless mode is appropriate and you have already tested recovery.
After a week of normal use, move additional accounts over gradually. This staged approach gives you real experience with your credential manager and devices before you depend on passkeys everywhere.
Frequently asked questions
Can someone steal my passkey if they know my device PIN?
If someone can unlock the device that contains or can access your passkeys, the risk is serious. Passkeys are designed to be protected by device security. Use a strong device PIN or passcode, enable biometric unlock where appropriate, and never share the device unlock code casually.
Do passkeys replace two-factor authentication?
A passkey can provide phishing-resistant authentication that combines device possession with local user verification. On some services, using a passkey satisfies the authentication requirement without a separate one-time-code step. The exact policy depends on the service and organization.
Can I have more than one passkey for the same account?
Many services allow multiple passkeys so you can register another device or a hardware security key. Some credential managers synchronize one passkey across several devices, so you may not need to create duplicates for every device. Review the service and provider behavior before adding unnecessary copies.
What happens if I lose my phone?
If the passkey is synchronized, it may be restored through your credential manager on another trusted device after you recover the provider account. If it is device-bound, you need another registered passkey or account-recovery method. This is why recovery planning comes before password removal.
Are fingerprints or face scans sent to websites?
Normally no. The biometric is used locally to authorize the device to use the passkey. Google explicitly states that biometric data used to unlock a Google Account passkey remains on the device, and FIDO specifications are designed so the service receives cryptographic proof rather than your biometric template.
Can I use a passkey on a computer that is not mine?
Yes, when the service and devices support cross-device authentication. Choose the option to use a passkey from another device, scan the QR code with your phone, approve the sign-in, and avoid saving the credential locally on the borrowed computer.
Should I delete every password after I create passkeys?
No. Remove passwords only when the service supports a true passwordless configuration and your recovery plan is proven. Otherwise keep a unique, long password in a password manager as a fallback while using the passkey for routine sign-in.
Are synced passkeys less secure than device-bound passkeys?
They have different trade-offs. Synced passkeys provide strong phishing resistance and better convenience and recovery for most consumers. Device-bound passkeys can offer tighter control in higher-assurance environments but require stronger operational planning because they do not automatically appear on replacement devices.
Can a passkey be copied by a phishing site?
A properly implemented FIDO passkey is bound to the legitimate service and is designed to resist phishing. A fake domain cannot simply ask you to type or reveal the passkey because there is no reusable secret to enter.
Why does a passkey prompt sometimes show several password managers?
Your operating system or browser may detect multiple credential providers. Choose the manager you actually use across your devices. If you accidentally save a passkey to the wrong provider, create a replacement in the preferred provider, test it, and then remove the unwanted credential.
Final checklist before you rely on passkeys
- Your phone and computer have strong screen locks and current software.
- You know which credential manager stores your passkeys.
- Your primary identity-provider account has a secure recovery route.
- You have at least one independent backup method for important accounts.
- You tested the passkey in a fresh browser session.
- You tested sign-in from another device.
- You understand whether the passkey is synced or device-bound.
- You did not save personal passkeys on a public or shared computer.
- You kept old sign-in methods until the new setup was proven.
- You know how to revoke a lost device and delete obsolete passkeys.
Sources and further reading
- FIDO Alliance: Passkeys — definition, security model, synced and device-bound passkeys.
- FIDO Alliance: User Authentication Specifications — FIDO2, WebAuthn, CTAP, privacy, and public-key authentication.
- CISA: More Than a Password — guidance on phishing-resistant MFA and FIDO/WebAuthn.
- Google Account Help: Sign in with a passkey instead of a password.
- Google Account Help: Use passwords and passkeys across your devices.
- Apple Support: Use passkeys to sign in to websites and apps on iPhone.
- Apple Support: Set up iCloud Keychain.
- Microsoft Support: Create and save a passkey.
- Microsoft Support: What are passkeys and why they matter.
- Microsoft Support: Manage your saved passkeys.
If you want the safest first move, do not try to convert every account at once. Start with one trusted device, one well-secured credential manager, and one important account. Add the passkey, test it from another device, and confirm recovery before removing anything. Once that pattern works reliably, repeat it. The security gain comes not from having the newest sign-in technology, but from knowing exactly where your credentials live, how they are protected, and how you will regain access when a device eventually fails or disappears.